Product updates

A clear record of what shipped.

Follow meaningful product changes across the starter, dashboard, billing, and AI workspace.

Latest release
v0.3.21
Release cadence
Continuous
Starter coverage
4 frameworks

More reliable sign-in and guest sessions

This update improves account isolation and fixes several issues in the Astro and SvelteKit templates.

What improved

  • Stronger guest isolation. Returning guests must have a valid session to recover their identity, helping keep each visitor’s data separate even when browser characteristics are similar.
  • Smoother sign-in recovery. Astro now renews an existing member session before starting a guest session, so an expired sign-in cookie does not unexpectedly switch a returning member into guest mode.
  • AI pages open correctly. The Astro dashboard now opens AI Playground and Image Agent as expected instead of showing the overview page.
  • More accurate multilingual checks. SvelteKit’s release checks now validate all seven supported public languages and their navigation, reducing false failures while continuing to catch missing translations and routing issues.

Upgrading an existing project

Update the authentication service first, then the Astro or SvelteKit templates used by your project. No database migration, new secrets, or additional service bindings are required.

Guest identity can no longer be recovered from a browser fingerprint alone. Existing valid guest sessions continue to work; visitors without a valid session may need to start a new guest session, subject to the usual access and free-credit limits.

0.3.20 — production rollout and security fixes

This release deploys the platform changes in the 19 official-repository commits from 957f5d4c through 724a82fb, plus the build and private-render binding compatibility fixes found during release verification. Version 0.3.19 documented committed work and explicitly did not deploy application Workers; 0.3.20 records the production rollout.

Release verification fixes are split into four functional commits: d25c11fb, 8f6e39cf, c80b4788, 3ff9277f.

Product changes

  • Next.js, TanStack, SvelteKit, Astro and Nuxt share the same backend for guest login, account conversion, protected workspaces, profiles, credits, orders, subscriptions, API keys and support. They include AI workspace and Image Agent entry points, with session-protected BFF routes.
  • Public pages include searchable/category-filtered blogs, readable articles, locale/theme controls and clearer pricing. Login preserves the destination and selected pricing plan, without automatically starting checkout.
  • Nuxt includes the Video Agent production workspace: project drafts, storyboards, scripts, reference assets, timelines, captions, voice revisions, render/export, delivery state and recovery.
  • Updated the official website, Admin, core Admin, landing sites and ZSaaS build artifacts. The repository also includes the consumer browser-extension template and contributor/deployment documentation; browser-extension distribution is separate from this Cloudflare rollout.

Security and business behavior

  • Provider1 task reads and actions enforce the authenticated tenant and owner. Core Store lists, details and downloads use the authenticated app scope; explicitly public * items remain supported. A caller-supplied app_key cannot select another tenant’s items.

  • Core Admin authentication and AI proxy routes enforce server-side authorization and route restrictions.

  • Guest risk checks account for shared IP budgets and credit limits. Admin magic links use trusted configuration, not the request’s x-admin-public-origin header. Set the trusted Admin origin before using email sign-in.

  • Paid decision/prompt-optimization requests reserve credits before model calls. Failed, uncertain and retried operations preserve their ledger identity.

  • Subscription refunds and chargebacks retain credit-lot identities and durable recovery state. Stripe cumulative refund tracking prevents repeated partial-refund credit revocation. Store and GitHub-access compensation is persisted for retry instead of relying only on logs.

  • AI and Provider media downloads go through the private Node12 egress binding with an operator-owned HTTPS origin allowlist, redirect checks and response validation. Add required provider media origins deliberately; missing origins fail closed.

  • The private renderer accepts trusted Service Binding calls without copying the public HTTP key. Public requests still require a configured ZSHIP_KEY; job callback tokens remain required. Node10 render submission/recovery no longer requires or forwards the public HTTP key.

  • Updated frontend toolchains and fixed release build compatibility: Astro prerendering resolves cookie 2.x explicitly; the website imports the Tailwind CSS entry explicitly and uses PostCSS plugin options. SvelteKit bundles its runtime cookie, serialization and Markdown dependencies to avoid incompatible hoisted versions. OpenNext Cloudflare is updated to 1.20.12 for Next.js 16.4.3, including the preview-props.json runtime compatibility fix.

  • Astro automatic guest sessions now use a random, app-scoped HttpOnly browser cookie instead of an IP/user-agent-derived fingerprint, so visitors sharing a network do not share a guest identity.

Database migration checklist

Apply these migration files in numeric order within each service before deploying its new code. This production account already had Node1 0046_admin_magic_link_rate_limit.sql; older installations must apply it before 0047.

  • node1-auth-service: 0047_credit_read_indexes.sql.
  • node10-ai-service: 0027_video_production_pipeline.sql, 0028_video_scene_jobs.sql, 0029_video_production_recovery.sql, 0030_video_render_attempts.sql, 0031_video_selective_reuse.sql, 0032_video_reference_assets.sql, 0033_video_production_reconciliation.sql, 0034_video_planning_dispatch.sql, 0035_video_production_delivery.sql, 0036_video_production_verification.sql, 0037_video_production_voice_revisions.sql.
  • node3-pay-service: 0017_subscription_credit_source.sql, 0018_stripe_refund_state.sql.
  • zship-core-service: 0011_credit_compensation.sql.
  • zship-provider1-service: 0040_provider_media_capabilities.sql, 0041_seed_video_production_models.sql, 0042_video_production_reference_input.sql, 0043_correct_video_provider_contracts.sql.

The Node10 files rebuild only the new video-production tables when needed and preserve the legacy video workflow. Provider1 seeds and contract corrections target platform defaults while retaining tenant settings and existing credentials. Back up database state and check applied migration names before running wrangler d1 migrations apply <database> --remote, which applies every pending file in the configured directory.

Bindings, secrets and rollout order

  1. Apply and verify the D1 migrations above. Preserve existing account-specific D1, KV, R2, queue, secret and service bindings.
  2. Deploy zship-node12-media-egress with MEDIA_EGRESS_ALLOWED_ORIGINS set to the approved provider and owned media origins; keep workers_dev: false, preview_urls: false and no public routes. Bind MEDIA_EGRESS on Node10 and Provider1 to this Worker.
  3. Deploy private zship-video-render with RENDER_JOB → RenderJob and its v1 SQLite Durable Object migration. Keep it without public routes. Bind Node10 VIDEO_RENDER_SERVICE to it. No new shared public key or secret rotation is required for this binding-only path.
  4. Deploy Node1 before Node3 and other credit callers. Configure Node1 ADMIN_PUBLIC_ORIGIN (this account uses https://admin.zship.ai); preserve ADMIN_SECRET, JWT_SECRET and any existing ZSHIP_KEY secret bindings.
  5. Deploy Node10 before Provider1 and support callers. Preserve IMAGE_AGENT_WORKFLOW, VIDEO_AGENT_WORKFLOW, private media R2/queues and IMAGE_AGENT_CREDENTIAL_KEY / IMAGE_AGENT_MEDIA_SIGNING_KEY. Add VIDEO_PRODUCTION_WORKFLOW → zship-video-production / VideoProductionWorkflow alongside VIDEO_RENDER_SERVICE and MEDIA_EGRESS.
  6. Deploy the affected payment, enterprise, Core, CDN, site, prompt, email, notification, blog, check-in and Cloudflare Admin services with their existing dependencies. Preserve the production notification queues, Node2 ERROR_REPORT_LIMITER and Node7 WAITLIST_JOIN_LIMITER. Core’s compensation retry cron is */15 * * * *; preserve other declared cron schedules.
  7. Deploy Admin, core Admin, the website and the five frontend templates after backend checks pass. Preserve frontend service bindings, the Nuxt content D1 database and Astro’s SESSION KV namespace.

Video Stream clipping additionally requires the operator’s VIDEO_STREAM_ENABLED, VIDEO_STREAM_ACCOUNT_ID, VIDEO_STREAM_API_TOKEN, VIDEO_STREAM_CUSTOMER_CODE and optional VIDEO_STREAM_TOKEN_TTL_SECONDS. Deploying the workspace does not configure a paid media provider, Stream account or model automatically. Browser export and Stream clipping are separate delivery modes; no server-side ffmpeg container was provisioned in this rollout. Production readiness checks confirm Stream clipping remains unconfigured on this account; this release does not enable that delivery mode.

Verification scope

Release checks cover backend types/tests, production builds, migrations, deployed bindings, service health and bounded authentication/media rejection checks. They do not create paid model generations, purchases, refund transactions, emails or support messages. Provider credentials, model availability and actual paid generation require the operator’s configured services and a separate live transaction test.

The bounded Astro guest check reached the test client’s daily guest credit allowance and correctly returned 429; the limit was not raised. Guest-browser isolation is covered by regression tests.
Product and template experience

  • Added one shared account contract across the five web templates: Next.js, TanStack, SvelteKit, Astro, and Nuxt now expose guest login, account conversion, protected workspaces, profile and balance views, subscriptions, orders, credits, API keys, and support entry points against the same ZShip backend.
  • Added workspace entry points for AI Playground/Studio and Image Agent. The adapters keep authentication, model discovery, streaming/chat requests, image-agent capabilities, conversations, turns, and turn-start operations on the existing backend services.
  • Added consistent localized auth routes for login, registration, verification, password recovery/reset, guest conversion, and session refresh. Protected route redirects preserve the intended destination and pricing plan selection.
  • Added the shared React workspace shell, account data views, mobile navigation, loading/error/empty states, theme and locale preferences, and the same account actions to the Astro and SvelteKit implementations through their native adapters.
  • Added public blog discovery with search and topic filters, readable article layouts, starter guides when the remote blog is empty, and locale-preserving navigation.
  • Added the latest Video Agent production workspace and editing flow in Nuxt, including projects, drafts, media, storyboard/timeline, captions, voice profiles, render/export, delivery, recovery, and version history.

Frontend and API contracts

  • Frontends now use explicit BFF allowlists for workspace, AI, Image Agent, authentication, and project routes. Account cookies are required before forwarding protected requests to the shared backend.
  • AI adapters expose model/config discovery and chat routes through the existing Node10 service bindings. Image Agent adapters expose capabilities, conversations, turns, and turn-start routes through the existing provider contract.
  • Pricing login handoff retains locale, return path, and the selected plan without starting checkout automatically after login. One-time credit packs remain separate from recurring subscription plans.
  • Account and blog views keep existing backend error responses visible, provide retry states, and avoid sending payments, emails, or support messages during client-side checks.

Backend changes and migrations

  • Node1 auth/credit ledger: apply backend/node1-auth-service/migrations/0046_admin_magic_link_rate_limit.sql and 0047_credit_read_indexes.sql in order. The admin credit reads are bounded and use the new indexes.
  • Provider1: apply 0040_provider_media_capabilities.sql, 0041_seed_video_production_models.sql, 0042_video_production_reference_input.sql, and 0043_correct_video_provider_contracts.sql in order.
  • Node10 AI: apply 0027_video_production_pipeline.sql through 0037_video_production_voice_revisions.sql in numeric order. These add video projects, scene jobs, recovery, render attempts, selective reuse, reference assets, reconciliation, planning dispatch, delivery, verification, and voice revisions.
  • The video path adds the Node12 media-egress service and the video-render service. Verify MEDIA_EGRESS, VIDEO_AGENT_WORKFLOW, VIDEO_PRODUCTION_WORKFLOW, and RENDER_JOB bindings before deployment.
  • Preserve existing NODE1_AUTH, NOTIFY_SERVICE, SUPPORT_SERVICE, PROVIDER1_SERVICE, and video service bindings. Apply D1 migrations, verify schema and health, deploy owners before callers, then deploy the five frontends last.
  • Keep secrets separate from plain vars and verify account-specific D1, KV, R2, service, workflow, and rate-limit resources before any production deployment.

Release state

This entry documents the committed platform update. The application workers were not redeployed as part of this data-only changelog operation. The migration inventory and owner-first deployment checks remain separate release work; verify guest login, workspace access, AI requests, Image Agent turns, and protected account routes on all five templates before promoting the corresponding workers.

Video Agent

  • node10 adds a Video Agent that runs on Cloudflare Workflows (zship-video-agent). It plans the shot, submits it through Provider1, tracks the provider task until it finishes, and supports cancel, retry, resume and a per-user video library. Routes live under /ai/video-agent/*.
  • Run credentials are encrypted with IMAGE_AGENT_CREDENTIAL_KEY (64 hex characters, the same secret Image Agent uses). Without it, Video Agent returns CREDENTIAL_ENCRYPTION_UNAVAILABLE.
  • Nuxt template: /dashboard/video-agent, shown in the dashboard nav when videoAgent.enabled is set in app.config.ts. Astro template: /video-agent.
  • node10 AI calls (chat completions, prompt optimization, decision models) now reserve the worst-case cost up front and refund the unused part when the call settles. Calls with an unclear outcome are reversed instead of charged twice, and stranded refunds are retried in the background.

Chrome extension template

apps/chrome-extension-template was rebuilt into a full consumer side panel:

  • Email, Google (chrome.identity) and guest sign-in, plus guest-to-account conversion that keeps trial credits.
  • Credits, billing (Stripe, Creem, Dodo, Waffo checkout and customer portal), settings, and an AI image studio demo with a “My images” gallery.
  • Refresh tokens rotate in the background worker with single-flight refresh. An API key is created silently after sign-in, so users never see one.
  • Page context (selection, URL, title) is read on demand behind an optional <all_urls> permission instead of running a content script on every page.
  • Developer tools are behind a hidden developer mode and are stripped from production builds unless WXT_DEV_TOOLS=true.
  • Mock mode for previewing every screen without a backend, English and Simplified Chinese, Vitest tests, and preflight:strict to catch demo branding and broad permissions before publishing.

Behavior changes to check before upgrading

  • CDN /public-upload now accepts only Service Binding calls or HTTP calls with x-zship-key matching node6’s ZSHIP_KEY secret. The x-proxy-source header is ignored. If the secret is missing, the route fails closed with 500.
  • Upload object keys are generated by the server as {namespace}/{folder}/{timestamp}-{32 hex}.{ext}. The filename field and the customFilename prop are ignored. /user-upload writes under user-uploads/ and /public-upload under public-uploads/. SVG is rejected on both, existing objects are never overwritten (409), and anything other than images, video and PDF is served as a download with nosniff and a sandbox CSP.
  • Provider1 /generate: safety fields (NSFW, safety checker, moderation) are set by the operator. They are hidden from /models and callers can no longer override them. Fields a model does not declare return 400 UNSUPPORTED_FIELD. Callback URLs must be public HTTPS on port 443; localhost, private and reserved IPs are rejected.
  • Checkout: the referralCode field in checkout requests is ignored. Commission now comes only from the referral bound in node1. A client baseUrl is honored only for the project’s own domain or subdomains over HTTPS, or for origins listed in node3’s new CHECKOUT_ALLOWED_ORIGINS. Anything else falls back to the project domain.
  • node2 /email/* is admin-only (admin.support). The from field is ignored, and tokens, JWTs and codes are redacted from logged and returned HTML.
  • Rate limits: node2 public error reports allow 30 requests per minute per IP with a 32 KB body limit. node7 waitlist joins allow 5 per minute per IP with a 4 KB limit. Over the limit you get 429, and oversized bodies get 413.

Payments: refunds, chargebacks and commissions

  • Partial refunds revoke buyer credits and referral commission in proportion to the refunded amount. Revocation is idempotent.
  • Chargebacks (Stripe charge.dispute.created, Creem dispute.created, Dodo dispute.opened / dispute.lost) revoke all credits and commission from the order and block the account from further payments in t_pay_account_block. Delete the row to unblock.
  • A coupon’s used_count now goes up only once the payment succeeds, not at checkout.

Accounts and guests

  • Converting a guest to a registered account now moves the guest’s API keys and Provider1 tasks to the new account. If the task transfer fails, a cron job retries it every hour at :30.
  • Taking over an unverified account (via email verification, Google or GitHub) revokes the API keys previously attached to that email. Revoked keys cannot be re-enabled, only replaced.
  • Google login: native clients send a raw nonce, and each nonce can be used only once. The existing web flow without a nonce keeps working.
  • Daily check-in credits are recorded as bonus, and zero-reward days no longer fail the check-in.

Migrations for self-hosted deployments

Apply before deploying the matching worker: Provider1 0038–0039 (before node1, which calls the task transfer); node1 0042–0045; node2 0013; node3 0016; node7 0005; node10 0020–0026.

Also check: node6 needs the ZSHIP_KEY secret; node1 needs the PROVIDER1 service binding; node2 and node7 need the new ratelimits bindings from wrangler.jsonc; node10 needs the VIDEO_AGENT_WORKFLOW binding.

Breaking changes for self-hosted deployments

  • Worker secrets are no longer in wrangler.jsonc. JWT_SECRET (node1) and ZSHIP_KEY (every worker that has it) were removed from plain vars. Before deploying this version, set them as secrets: wrangler secret put JWT_SECRET on node1, and one shared, strong ZSHIP_KEY on node1, node2, node3, node9, node10, node11, Provider1 and Enterprise Billing. If you deployed earlier versions without replacing the placeholders, rotate both now: the defaults are public. For local development, copy each service’s .dev.vars.example to .dev.vars (the dev console does this for you).
  • apps/web was removed. The Astro template now lives in apps/web-astro. Move your customizations there before updating.
  • The template /changelog page reads local Markdown. Add entries as Markdown files with version, title and date frontmatter, one folder per locale: content/changelog/ in Nuxt, src/content/changelog/ in Astro, SvelteKit and TanStack (see each template’s README). The ZSHIP_CORE_SERVICE binding is internal to ZShip and is no longer part of the templates.
  • Custom domains are no longer preset. node6 and node10 no longer ship cdn.zship.ai / media.zship.ai routes. Add your own routes, and set IMAGE_AGENT_MEDIA_PUBLIC_URL on node10; until it is set, Image Agent media returns IMAGE_MEDIA_NOT_CONFIGURED.

Test accounts

  • Admin → Test Accounts creates a test user for a project, with optional seeded credits, a subscription and one-time orders taken from the project’s price config.
  • Each account gets a reusable sign-in link (1–90 days, default 7) that opens the site already signed in. The token is shown once; links can be reissued or revoked, and accounts can be disabled.
  • Test orders use the test provider. They appear in the order history but are excluded from revenue, order and paying-user statistics, and never send paid-order notifications or create affiliate commissions. Cancelling, resuming or changing a test subscription is simulated without calling Stripe.
  • Supported in the Nuxt and Astro templates at /auth/test-login.

Credits

  • Subscription credits are now spent before permanent credits.
  • Failed generation refunds return credits to the bucket they were taken from, with the original expiry. If those subscription credits have already expired or been reset, that part is not refunded.

Image Agent

  • KIE Nano Banana 2 accepts up to 14 reference images, so the Agent can edit an existing image instead of regenerating it from text.
  • Uploaded references and results are stored privately per user and served through short-lived signed links on a dedicated media host.

Decision models

  • Admin → AI → Decision maps scenarios (moderation, support tickets, feedback) to Cloudflare Clef models with per-scenario pricing. Provider image moderation and support ticket triage can use them.

Migrations for self-hosted deployments

Apply before deploying the matching worker: node1 0041_test_accounts.sql; Provider1 0035–0037; node10 0018–0019; node2 0012.

Dodo Payments and Waffo Pancake

  • The payment service now supports Dodo Payments and Waffo Pancake alongside Stripe and Creem. Both are integrated over their REST APIs without adding an SDK dependency.
  • Checkout, customer portal links, and webhooks cover one-time credit packs, subscription activation and renewals, cancellations, and refunds. Credits are granted and revoked with the same idempotency rules as the existing providers.
  • Webhooks must be signed: Dodo requests are verified with Standard Webhooks HMAC signatures, and Waffo requests with RSA signatures against the Waffo platform public keys. Unsigned or invalid requests are rejected.
  • The official Nuxt, Astro, TanStack, and SvelteKit templates send checkout to whichever provider is bound to the project.

Where to configure

  1. Admin → Pay Channels: create a Dodo channel (API key, webhook signing secret, test or live environment) or a Waffo channel (Merchant ID and API private key).
  2. Admin → Projects → Edit project → Payment: bind the channel. Each project uses one provider.
  3. Admin → Price Config: fill in the Dodo product ID (pdt_…) or the Waffo product ID (PROD_…).
  4. In the provider dashboard, register the webhook URL https://<node3>/dodo/webhook or https://<node3>/waffo/webhook. For Waffo, register it once for test and once for production.

Notes

  • ZShip coupons are not applied to Dodo or Waffo checkout yet, so the pricing page hides coupon entry for those providers.
  • In-app plan changes and cancellation remain Stripe-only. Dodo and Waffo subscribers manage their subscriptions in the provider portal.
  • Self-hosted deployments need the node3 D1 migration 0015_dodo_waffo_providers.sql before deploying the new code.

Image Agent

  • The official Nuxt dashboard now includes an Image Agent for discussing images, generating new ones, and editing existing ones.
  • Accepted work continues on the server if you leave the page. You can reconnect to the same run or stop it, and the workspace shows the credits used by the selected image model.
  • Reference images can be added by upload, link, or the material library. Generated images keep their version history.
  • Image models whose provider has no durable image delivery can now be used as well; their results keep the provider’s image URL.

Open Dashboard → Image Agent (/dashboard/image-agent).

Admin

  • Admin → AI → Image Agent sets the Agent’s model, the on/off switch, and per-run limits for steps, operations, and credits.
  • Provider task rows created by the Agent now link to the dialogue charges of that run.

Project-level daily free credit caps

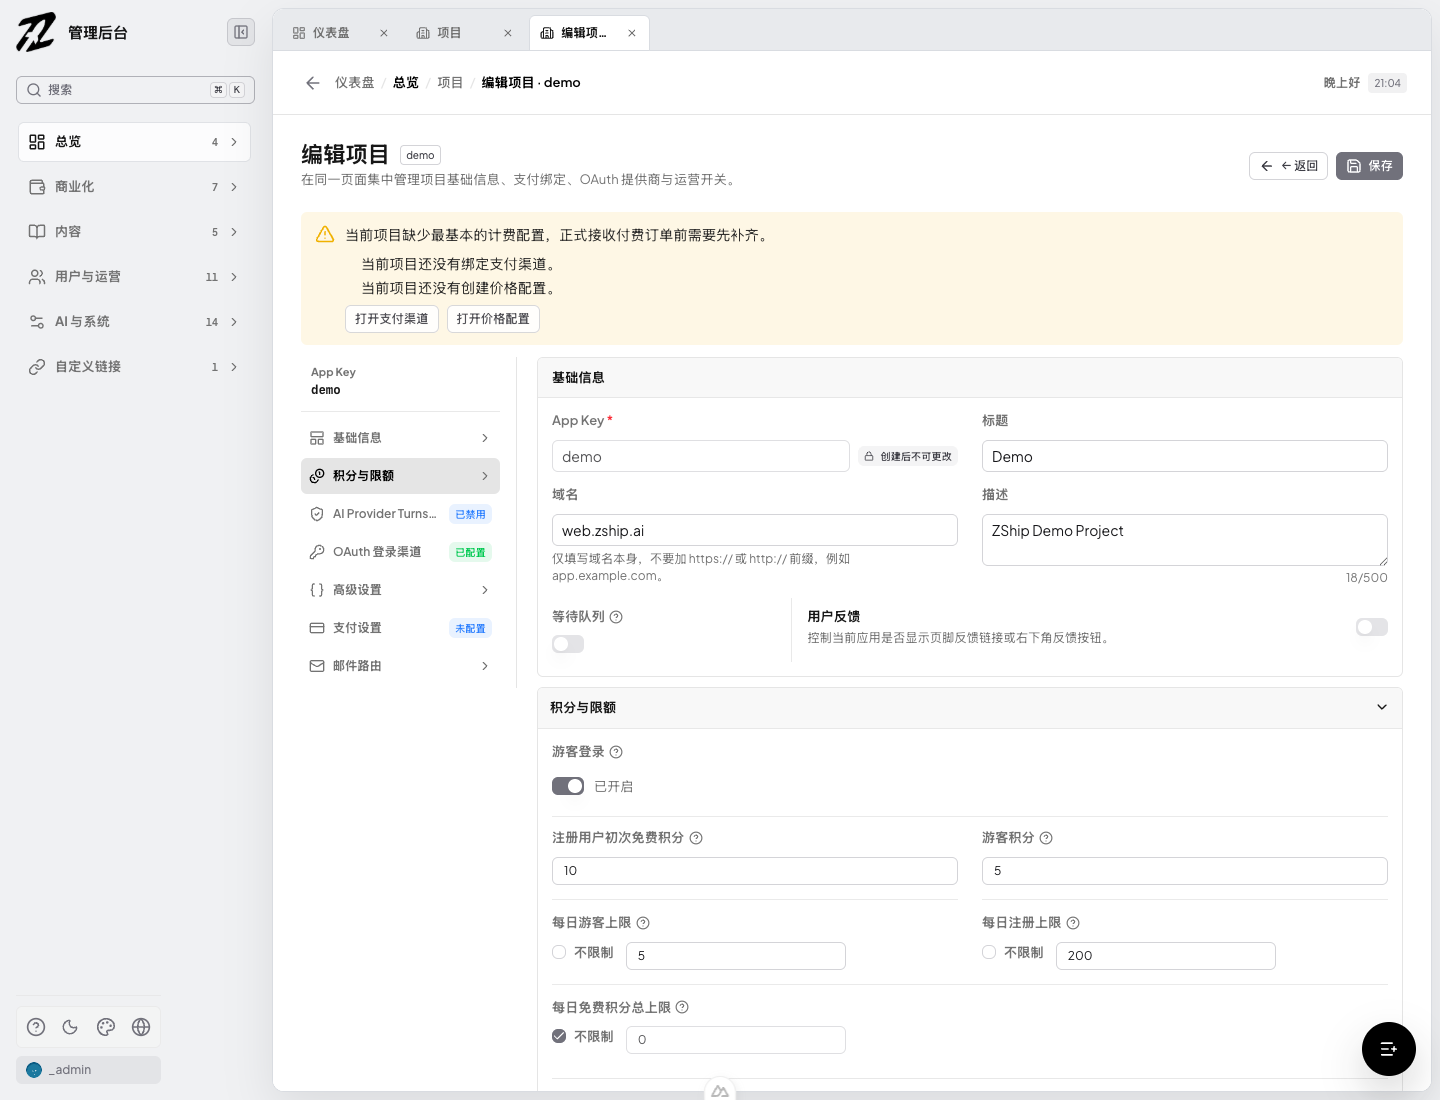
  • Admin project settings can now set a daily free-credit cap for each project; 0 remains unlimited.
  • The cap combines initial credits issued to guests and registered users within each UTC day, so switching account type cannot bypass the project budget.
  • Requests that would exceed the cap are rejected before credits are granted, while an atomic D1 guard protects concurrent requests from over-issuing credits.

Where to configure

Open Admin -> Projects -> Edit project -> Credits & limits to set the daily guest, registration, and aggregate free-credit caps.

Daily free credit limit settings in the ZShip Admin

Seven new AI models and Qwen branding

  • Added seven ready-to-use model configurations to AI Playground: WaveSpeed Seedance 2.5, Qwen Image 3.0, and MiniMax H3; plus KIE Seedance 2.5, MiniMax H3, Qwen3 text-to-image, and Qwen3 image-to-image.
  • Model availability is loaded dynamically from the provider service, so newly enabled models appear after a refresh without requiring a separate frontend release; cached sessions may take up to five minutes to refresh.
  • Corrected Qwen model branding to use the official Qwen logo instead of the Alibaba Cloud group mark.
  • WaveSpeed models require a WaveSpeed API key to be configured before generation requests can succeed.

Safer official templates and stronger release checks

  • Synced the official Nuxt, TanStack Start, SvelteKit, and Astro templates to the current product-quality baseline while preserving repository-specific configuration.
  • Strengthened BFF and proxy contracts for tenant-scoped requests, authenticated routes, and guest-access switches, with dedicated CI coverage for critical flows.
  • Hardened CDN CORS handling and blog rendering so public content behaves consistently across supported origins and localized routes.
  • Expanded SEO and GEO output with localized canonical URLs, structured data, sitemap and llms.txt checks across the official templates.
  • Made SvelteKit type checks reproducible in clean CI environments instead of relying on generated local cache state.
  • Verified the release with template manifests, unit and proxy-contract tests, critical-path checks, i18n/SEO validation, and production builds for all four frontend templates.

Template productization & quality baseline

  • Unified zship.app.json schema and validator (@zship/app-manifest) so full-saas and static-content templates share one contract before scaffold or deploy.
  • First-class scaffolding for SvelteKit and TanStack Start via create-zship / scaffold-core, with Dev Console and skill docs aligned to the new profiles.
  • TanStack templates load landing locales and heavy dashboard modules on demand, with bundle budget checks to keep the first paint lean.
  • Locale and SEO gates cover required strings, sitemap/llms.txt, and critical marketing routes across templates.
  • CI template:check, scaffold smoke tests, and a desktop/mobile · light/dark · en/zh-CN critical-path matrix lock the quality bar.
  • SvelteKit and TanStack hotspots (AI studio, playground, pricing, enterprise billing, OAuth/proxy helpers) are split into API/state/view layers with unit coverage.
  • Preview baselines are live for TanStack, SvelteKit, Nuxt, and Astro on *.zship.ai.

Faster, more reliable AI creation

  • AI Provider model metadata is now available in server-rendered pages, helping public AI tools describe their real capabilities to search engines before JavaScript loads.
  • Provider model and Turnstile configuration reads now use browser TTL caching, while identical in-flight requests are merged instead of sent repeatedly.
  • AI history reads are concurrency-limited, generation requests are serialized and protected from duplicate submissions, and abnormal pagination can no longer continue indefinitely.
  • Task status polling now backs off progressively, adds jitter, pauses when the page is hidden, and stops after repeated failures, reducing unnecessary Cloudflare requests and extra usage.

Reliable notification delivery

  • Production notifications now run through Cloudflare Queues with automatic retries and a dead-letter queue for deliveries that cannot be completed.
  • Idempotent processing prevents duplicate delivery, while failure isolation keeps one failed job from blocking the rest of a batch.

Queue operations in Admin

  • Admin now includes an account-wide Queue inventory showing Queues, dead-letter queues, Workers, producer bindings, and consumers in one place.
  • Operators can view live Queue and DLQ metrics, send a real test message, and inspect or manage failed deliveries.
  • Topology views and search make it easy to trace a Queue by Worker, binding, Queue, or DLQ name.

Experience and development

  • Queue management is responsive across desktop and mobile, supports light and dark themes, and is available in English, Simplified Chinese, and Traditional Chinese.
  • Local development startup is more reliable, with the Node4 notification service consistently using port 8790.

Cloudflare control plane and R2 management

  • Admin adds an account-wide inventory for Workers, Pages, D1, KV, R2, and Queues, with independent capability and permission diagnostics so one unavailable product does not hide the rest.
  • Authorized operators can inspect R2 account and bucket settings, change the default storage class, manage r2.dev and custom-domain access, and maintain lifecycle and CORS policies through allowlisted, confirmed actions.

Guided operations

  • Email Service includes a copy-ready AI setup guide with explicit authentication, account-isolation, secret-handling, test-delivery, and rollback safeguards while keeping Resend as the production primary provider.
  • The Provider page now explains why task orchestration continues to use Cron, Queues, and D1 instead of Cloudflare Workflows, making the current reliability and cost tradeoff visible to operators.

Admin experience and session safety

  • AI management translations are complete across supported Admin locales, and the stale Queue availability label has been removed.
  • Expired or rejected Admin sessions now clear local session state and return directly to the locale-aware login page instead of the 403 page, including SSR navigation without redirect loops.

Native Workers AI and safer model rollout

  • ZShip AI now runs through Cloudflare’s native Workers AI binding while preserving the existing OpenAI-compatible JSON and SSE streaming APIs.
  • Admin includes a complete model workflow for syncing the Workers AI catalog, setting credit prices, running gray validation, and enabling or disabling each model. New models remain disabled until pricing and validation are complete.
  • AI Gateway requests carry traceable request and application metadata without retaining request or response payloads. Billing is idempotent, streamed cancellations are recorded, and rate-limit or provider failures remain visible in logs.
  • The production catalog contains 19 valid model entries, with 15 commonly used text models enabled and priced by cost. Later catalog syncs automatically disable models that Cloudflare has retired.

Provider task status in public APIs

  • Provider1 task list and status responses now include provider_status, allowing clients to distinguish upstream provider progress from the ZShip task state.
  • The field is available in both list items and task details, and remains present when completed-task responses are served from cache.
  • The deployed Provider1 API was verified against an existing completed task; list, live status, and cached status responses all returned the upstream SUCCESS state.

Rollout notes

The native Workers AI database migrations, zship-node10-ai Worker, and Admin application are live in production. Real non-streaming and SSE streaming inference, the model catalog, service bindings, and Admin health checks were verified after deployment.

Admin workspace and platform reliability

  • The Admin workspace now uses layered tabs and integrated navigation. Parent groups open compact icon-and-label menu matrices, with responsive mobile layout and light and dark themes.
  • Provider generation workflows now keep stable idempotency context across creation, polling, webhooks, credit deductions, and result transfer to prevent duplicate work and duplicate charging.
  • Resend delivery now balances traffic across eligible keys with daily quota awareness, while Admin exposes key health, routing preference, usage, and delivery logs.
  • Provider configuration supports batch updates with deliberate cache invalidation, and subscription credit jobs use bounded queries and processing budgets for more predictable scheduled runs.

Creative Studio canvas polish

  • Creation cards show open / use-as-reference / delete on desktop hover (always visible on touch devices).
  • Removed the media-type corner badge for a cleaner gallery.
  • Deleting a creation opens an in-app confirmation modal with thumbnail and title, instead of the browser native confirm dialog.
  • Soft-delete in production; mock mode removes items locally after confirm, with loading protection against double submit.
  • Delete-related copy is localized for English, Simplified Chinese, Traditional Chinese, Japanese, and Korean.

Concurrent AI generation in Quick Create

  • Preview stays focused on the latest generation task, while you can switch earlier tasks from the task list.
  • Running tasks keep polling independently, so starting a new generation no longer stops progress updates for earlier jobs.
  • Single-run multi-image results stay on one result card with a desktop grid and mobile stack layout.
  • Mock image models now support generating 1–4 images per run (default 4), with credits charged per image.
  • Refined Quick Create result actions: hide the canvas title, keep result tabs right-aligned, and show card actions on desktop hover while always showing them on touch devices.
  • Completed empty-state i18n for AI assets across English, Simplified Chinese, Traditional Chinese, Japanese, and Korean.

Device-level authentication security

  • Added per-device access and refresh session families with credential rotation, replay isolation, and selective revocation.
  • Added active-session visibility and controls for users and administrators, plus server-side version checks for admin and guest sessions.
  • Hardened registration by separating email verification from password setup, preventing unverified-account takeover, and moving GitHub OAuth state to server-managed one-time credentials.

Refined AI workbench

  • Finalized the responsive full-canvas Playground for desktop and mobile with provider-defined UI metadata and samples.
  • Unified generation history with the asset library and improved empty, unavailable, progress, and result states across light and dark themes.
  • Improved Admin user session management, modal hierarchy, responsive layout, multilingual copy, D1 migrations, and auth/provider regression coverage.

Refined AI creation workspaces

  • Clarified the roles of Quick Create and Creative Studio with a shared model picker and consistent generation interactions.
  • Redesigned Quick Create with a cleaner prompt composer, compact media upload, creative canvas, duration slider, and clearer generation cost action.
  • Improved Creative Studio history density and responsive behavior across desktop, mobile, light, and dark themes.
  • Added complete local mock flows for image, video, and audio generation, including submission, polling, results, and reusable assets.

Read the implementation docs

Need setup details? The docs cover configuration, services, and deployment.

Docs